Testing laboratory and consultancy · Granges-Paccot

Book a call

Cybersecurity · Connected products

Cybersecurity of connected products

Connected devices, machinery, electronic equipment: as soon as a product exchanges data, it must withstand attacks and be able to prove it. Säfeli analyses the threats, assesses your product against the Radio Equipment Directive (RED) and the Cyber Resilience Act, tests it the way an attacker would and helps you fix what needs fixing, from design to placing on the market.

RED cybersecurity mandatory
01.08.2025
CRA vulnerability reporting
11.09.2026
Cyber Resilience Act applies
11.12.2027
Support period, as a rule
5 years

Who it is for

You make products that communicate

  • Connected devices

    Smart home, wearables, consumer IoT: RED, personal data, CRA.

  • Machinery and industrial equipment

    Remote maintenance, factory network, safety software: Machinery Regulation and IEC 62443.

  • Electronics and components

    Routers, gateways, sensors, modules: CRA classes and integrator requirements.

  • Hardware start-ups

    A first connected product: security by design, so you do not have to redo everything before launch.

Our services

Securing your product, from design to placing on the market

Threat analysis, regulatory assessment and penetration testing: the three building blocks for demonstrating the cybersecurity of your product.

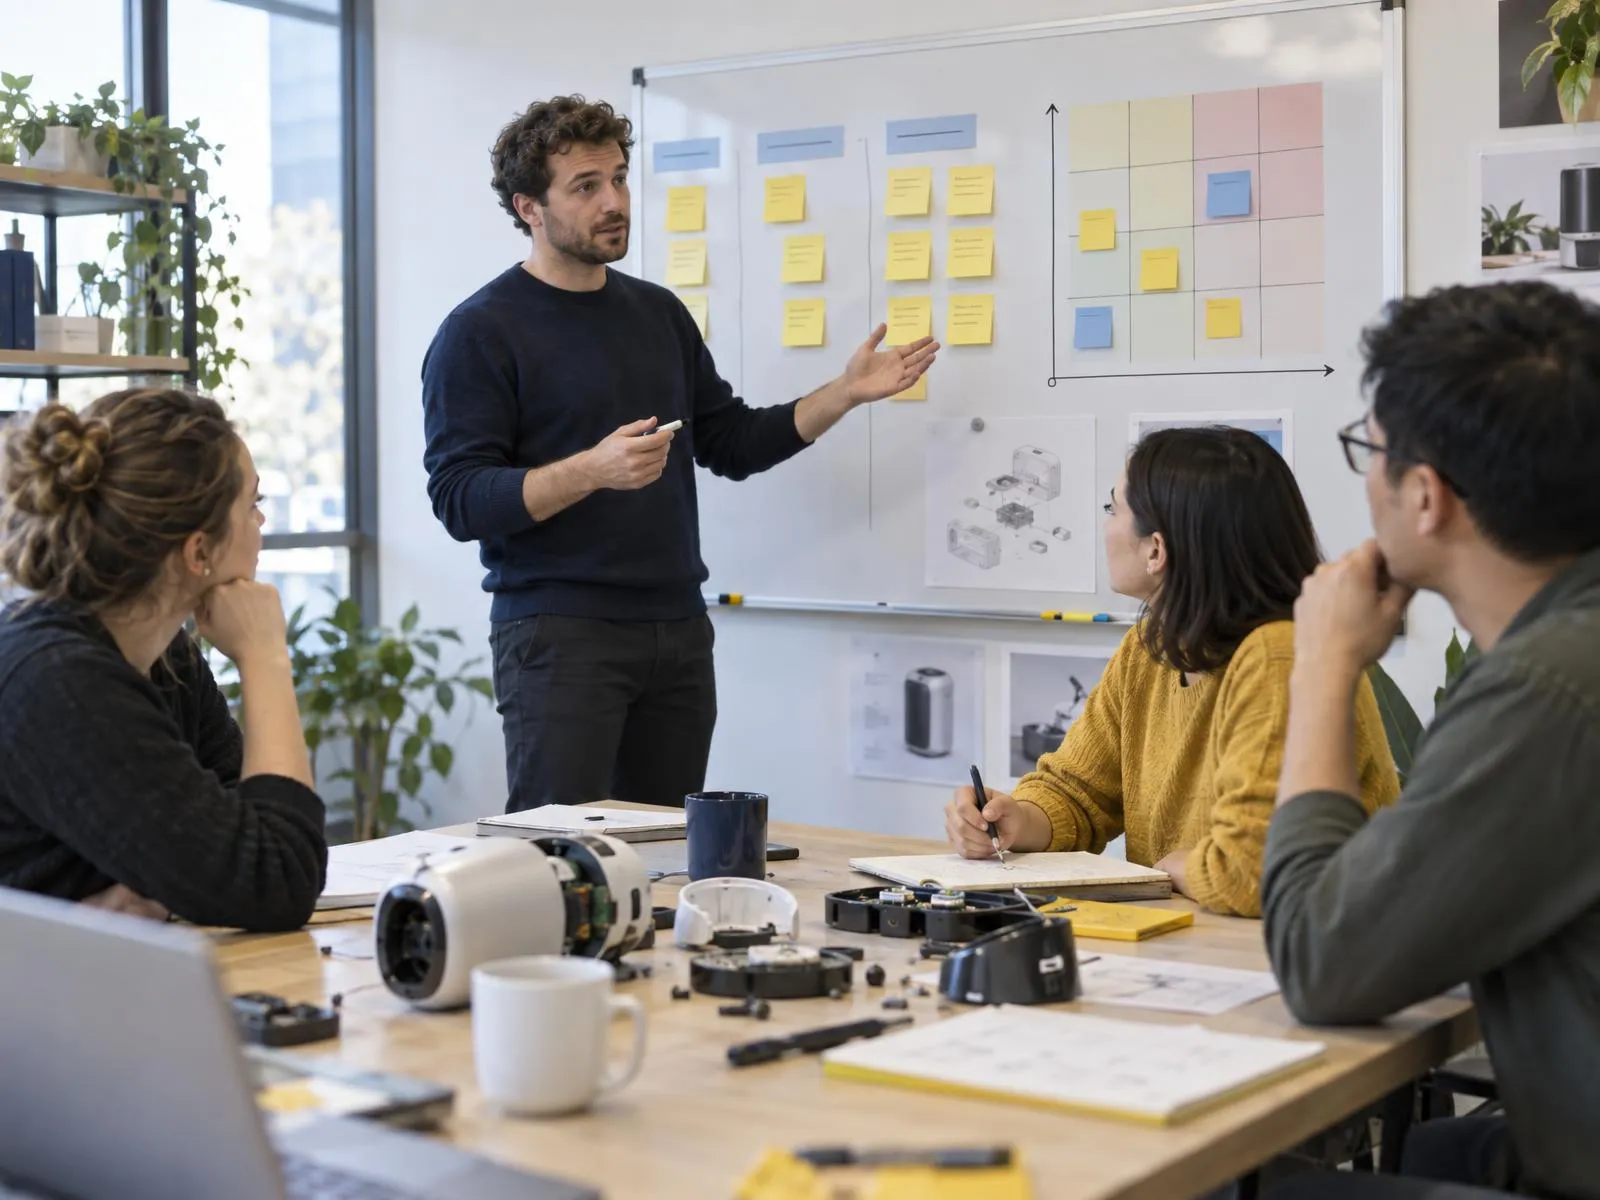
Threat analysis workshop with a design team
Threat analysis

Threat analysis (TARA)

Assets, interfaces, threats, attack scenarios: the cybersecurity risk assessment is the foundation required by the Cyber Resilience Act and the starting point of EN 18031. We carry it out with your teams, from the design stage.

What you receive

  • Model of the product and its interfaces
  • Attack scenarios and risk assessment
  • Security requirements to implement

References

  • CRA, Art. 13(2) to (4)
  • IEC 62443-3-2:2020
Threat analysis in detail
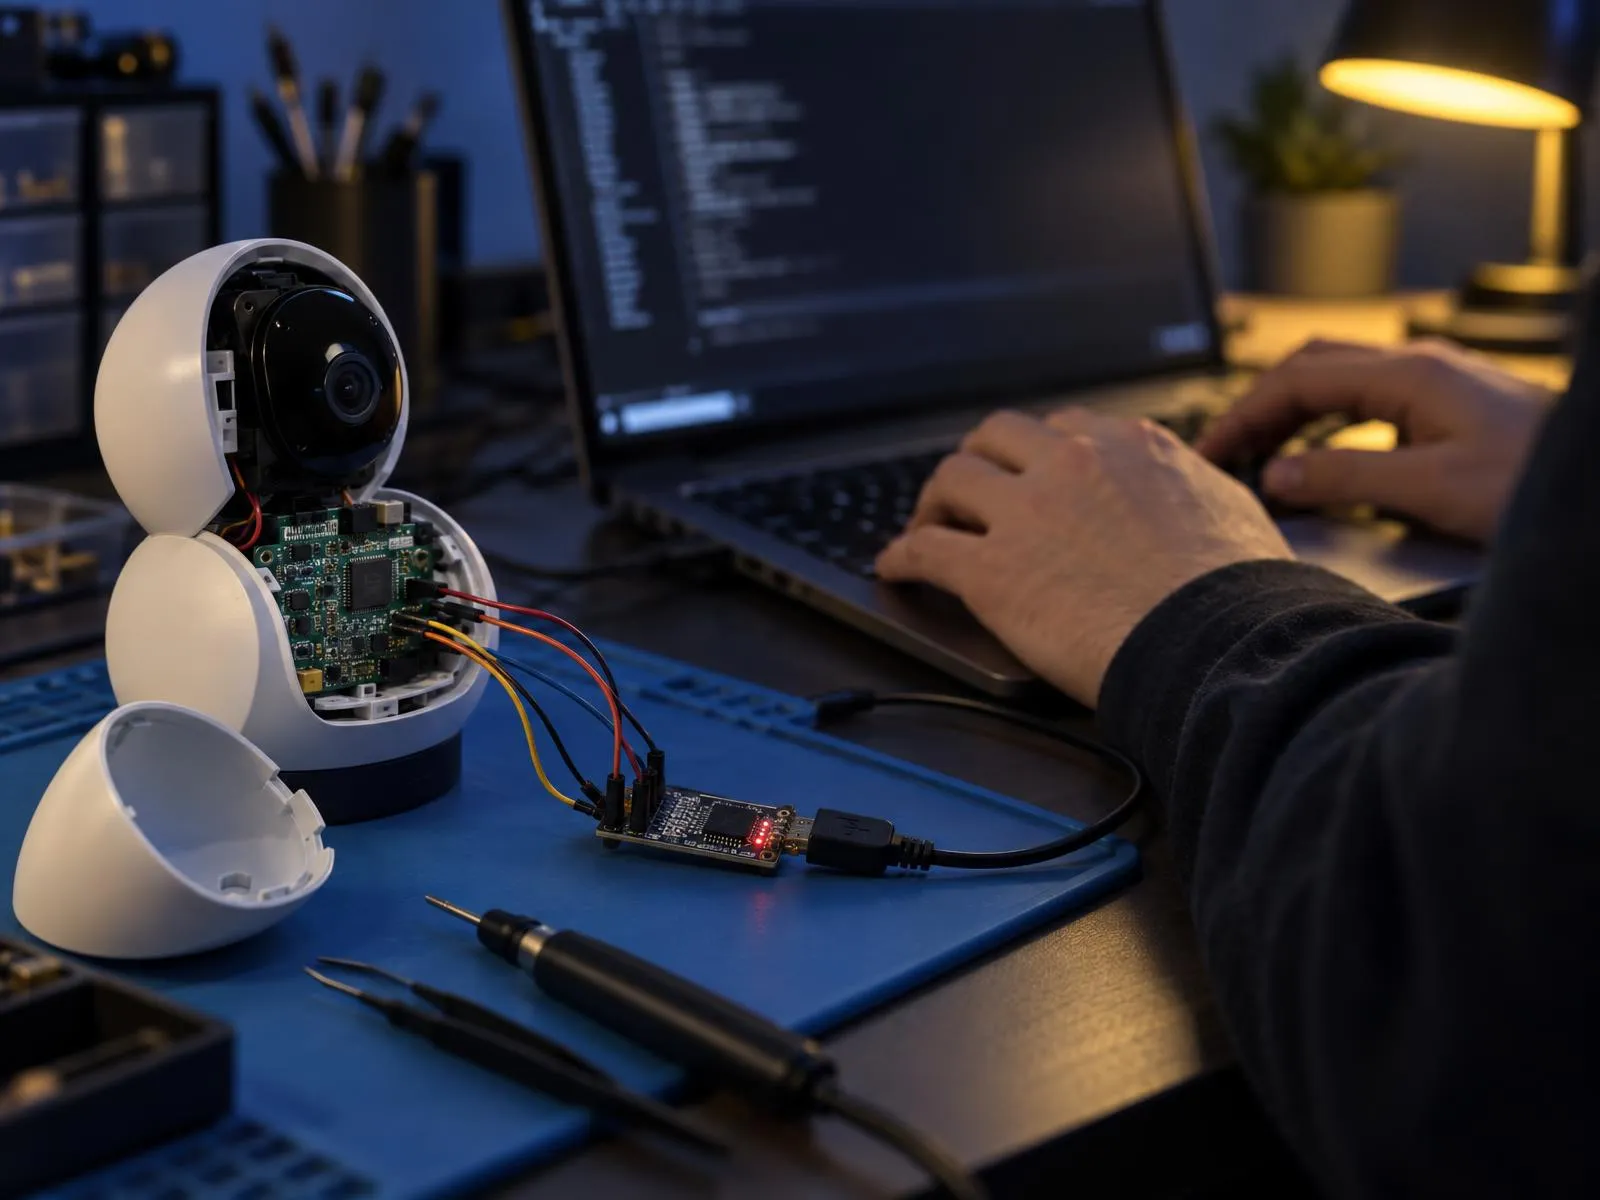
Opened connected camera linked to a computer for a security assessment
Radio Equipment Directive

Radio Equipment Directive (RED) and EN 18031

Since 1 August 2025, radio equipment connected to the internet must protect the network and personal data and, if it allows payments, guard against fraud. We assess your product against EN 18031 and help you close the gaps.

What you receive

  • Applicable requirements: points (d), (e) and (f)
  • EN 18031 assessment, mechanism by mechanism
  • Documentation for the technical file

References

  • Delegated Regulation (EU) 2022/30
  • EN 18031-1:2024
The RED and EN 18031
Engineer reviewing an inventory of software components and a list of vulnerabilities
Cyber Resilience Act

CRA compliance

Essential requirements, vulnerability handling, software bill of materials (SBOM), reporting, documentation: we assess your product against the Cyber Resilience Act and build with you the processes required before 11 December 2027.

What you receive

  • Scope, class and conformity assessment procedure
  • Gap analysis against the essential requirements
  • Vulnerability handling process

References

  • Regulation (EU) 2024/2847
The Cyber Resilience Act in detail
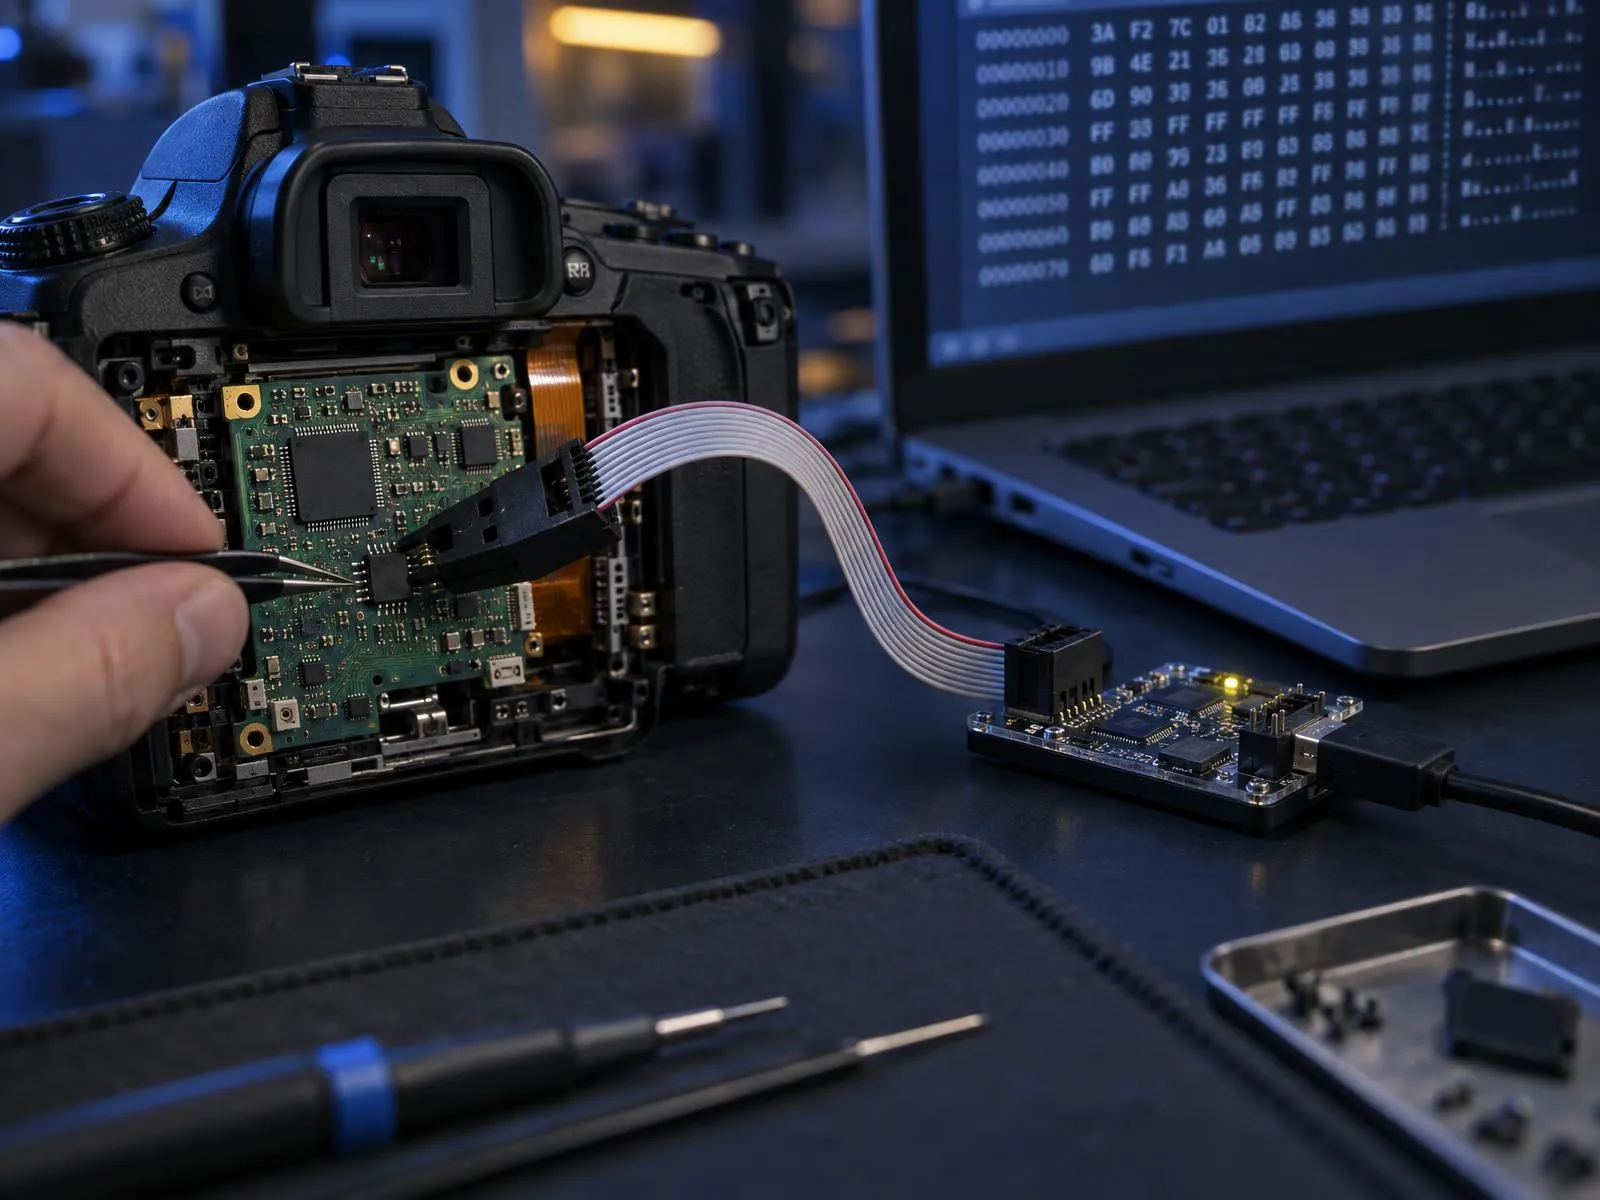
Test clip on the flash memory of a device, linked to a programmer and a computer
Penetration testing

Product penetration testing

Hardware interfaces, firmware, radio, app and cloud: we attack your product the way an attacker would, to find the vulnerabilities before they do, and give you practical recommendations.

What you receive

  • Test plan tailored to the product
  • Report of vulnerabilities ranked by severity
  • Retest after fixes

References

  • OWASP IoT Security Testing Guide
  • IEC 62443-4-1:2018
Our product penetration testing

Also

Regulation

What the EU requires of a connected product

Two pieces of legislation follow one another: the Radio Equipment Directive (RED) for radio equipment connected to the internet, then the Cyber Resilience Act for all products with digital elements. The work done for one serves as the basis for the other.

  1. 01.08.2025RED: cybersecurity requirements
  2. 11.09.2026CRA: reporting of vulnerabilities and incidents
  3. 11.12.2027CRA: full application, end of the RED cybersecurity part
  • RED: three cybersecurity requirements

    Radio equipment connected to the internet: protection of the network, of personal data and, for payments, against fraud. Demonstrated with the EN 18031 series.

    Delegated Regulation (EU) 2022/30
  • CRA: design requirements

    Secure by default, access control, encryption, integrity, updates, reduced attack surface: based on a cybersecurity risk assessment.

    CRA, Art. 13; Annex I, Part I
  • CRA: vulnerability handling

    Software bill of materials (SBOM), regular testing, coordinated disclosure, free security updates throughout the support period, as a rule at least five years.

    CRA, Annex I, Part II; Art. 13(8)
  • CRA: reporting

    Actively exploited vulnerabilities and severe incidents: early warning within 24 hours, notification within 72 hours, via ENISA's single reporting platform. This also applies to products already on the market.

    CRA, Art. 14 and 69
  • CRA: product classes

    Routers, security cameras, smart locks, connected toys…: for certain important and critical products, a third party is involved in the conformity assessment.

    CRA, Art. 7, 8 and 32; Annexes III and IV
  • The CRA takes over

    On 11 December 2027, the cybersecurity part of the Radio Equipment Directive is repealed; the CRA then applies to all products with digital elements, radio or not.

    Delegated Regulation (EU) 2026/339

Sources: Delegated Regulation (EU) 2022/30; Regulation (EU) 2024/2847, Art. 7, 13, 14, 32, 69 and 71, Annexes I, III and IV; Delegated Regulation (EU) 2026/339.

CE marking

Cybersecurity, part of CE marking

Cybersecurity requirements come on top of the other CE marking requirements: electrical safety, EMC, radio, machinery safety. We handle them together, in a single certification plan and a single technical file, so that you have just one point of contact.

Standards

Product cybersecurity standards

The EN 18031 series serves the Radio Equipment Directive; the harmonised standards for the CRA are in preparation. The IEC 62443 and ETSI standards complete the state of the art.

FieldStandardScope
REDEN 18031-1:2024Internet-connected radio equipment: network protection (Art. 3.3(d))
REDEN 18031-2:2024Protection of personal data (Art. 3.3(e))
REDEN 18031-3:2024Protection from fraud (Art. 3.3(f))
CRAEN 40000 series (in preparation)Harmonised standards for the CRA, standardisation request M/606
IndustryIEC 62443-3-2:2020Cybersecurity risk assessment for system design
IndustryIEC 62443-4-1:2018Secure product development lifecycle
IndustryIEC 62443-4-2:2019Technical security requirements for components
IoTETSI EN 303 645 V3.1.3Cybersecurity for consumer IoT (non-harmonised reference)
IoTETSI TS 103 701*Conformity assessment against ETSI EN 303 645
TestingOWASP ISTG v1.0.1Security testing guide for connected devices

* Version to be checked for your project. The EN 18031 series gives presumption of conformity with the Radio Equipment Directive within the limits of the restrictions published in the Official Journal of the EU. Until the harmonised standards for the CRA are cited in the Official Journal of the EU, CRA compliance is demonstrated by other means, which we document with you.

Our approach

Your product cybersecurity in four steps

  1. Discovery call

    Your product, its connections, your markets and your timeline. 30 minutes.

  2. Analysis

    Applicable legislation, class, threat analysis, assessment and test plan.

  3. Assessment and testing

    EN 18031, CRA requirements, penetration testing, fixes with your teams.

  4. Technical file

    Technical documentation, vulnerability handling process, EU declaration of conformity.

Swiss market

Product cybersecurity in Switzerland

Switzerland does not yet have an equivalent of the Cyber Resilience Act: on 25 September 2026, the Federal Council decided to create a federal cybersecurity act modelled on the CRA, with a draft to be put out for consultation by June 2027. The cybersecurity requirements of the Radio Equipment Directive, however, have already been adopted in the OFCOM Ordinance on Telecommunications Installations (VFAV).

A Swiss product sold in the EU must comply with the CRA like any other product: we can prepare you for it now.

Sources: Federal Office for Cybersecurity (BACS), press release of 25.09.2026; VFAV, SR 784.101.21, Annex 1, items 7 to 9.

Frequently asked questions

Frequently asked questions on product cybersecurity

Does your product raise a specific question? Ask an engineer directly.

Book a call
Is my product covered by the Cyber Resilience Act?

Very probably, if it contains software and can exchange data, directly or indirectly, with a device or a network: connected device, machine, electronic equipment, software sold as a product. A few sectors have their own rules and are excluded, such as medical devices, vehicles and certified aeronautical products.

Sources: Regulation (EU) 2024/2847, Art. 2 and 3

When does the Cyber Resilience Act apply?

It entered into force on 10 December 2024. The obligations to report actively exploited vulnerabilities and severe incidents have applied since 11 September 2026; the regulation as a whole applies from 11 December 2027.

Sources: Regulation (EU) 2024/2847, Art. 71

Radio Equipment Directive or Cyber Resilience Act: which one applies?

Today, radio equipment connected to the internet must meet the cybersecurity requirements of the Radio Equipment Directive, which have applied since 1 August 2025. On 11 December 2027, these requirements are repealed and the Cyber Resilience Act takes over, for all products with digital elements, radio or not.

Sources: Delegated Regulations (EU) 2022/30 and 2026/339; Regulation (EU) 2024/2847

Do I need a notified body?

For most products, no: the manufacturer assesses conformity itself. For important products of class I, this is possible only by fully applying harmonised standards or a certification scheme; otherwise, a notified body is involved. For class II and critical products, a third party is always required.

Sources: Regulation (EU) 2024/2847, Art. 32

For how long must security updates be provided?

Throughout the support period, which the manufacturer sets according to the product's expected period of use: at least five years, unless the product is expected to be used for a shorter time. Each security update released must then remain available for at least ten years.

Sources: Regulation (EU) 2024/2847, Art. 13(8) and (9)

What about Switzerland?

Switzerland does not yet have an equivalent of the CRA: on 25 September 2026, the Federal Council decided to create a federal cybersecurity act modelled on the CRA, with a draft to be put out for consultation by June 2027. The cybersecurity requirements of the Radio Equipment Directive have already been adopted into Swiss law. A product sold in the EU must comply with the CRA in any case.

Sources: Federal Office for Cybersecurity (BACS), press release of 25.09.2026; VFAV, SR 784.101.21, Annex 1

Book a call

Tell us about your connected product

Book a 30-minute slot with an engineer directly. No back-and-forth by email: you choose the time, we prepare the call.

Choose a time slot

Contact details

Address
Säfeli Sàrl
Route d'Englisberg 3
1763 Granges-Paccot
Languages
French, German, English
Book a call