Hardware and firmware
Hardware interfaces and firmware
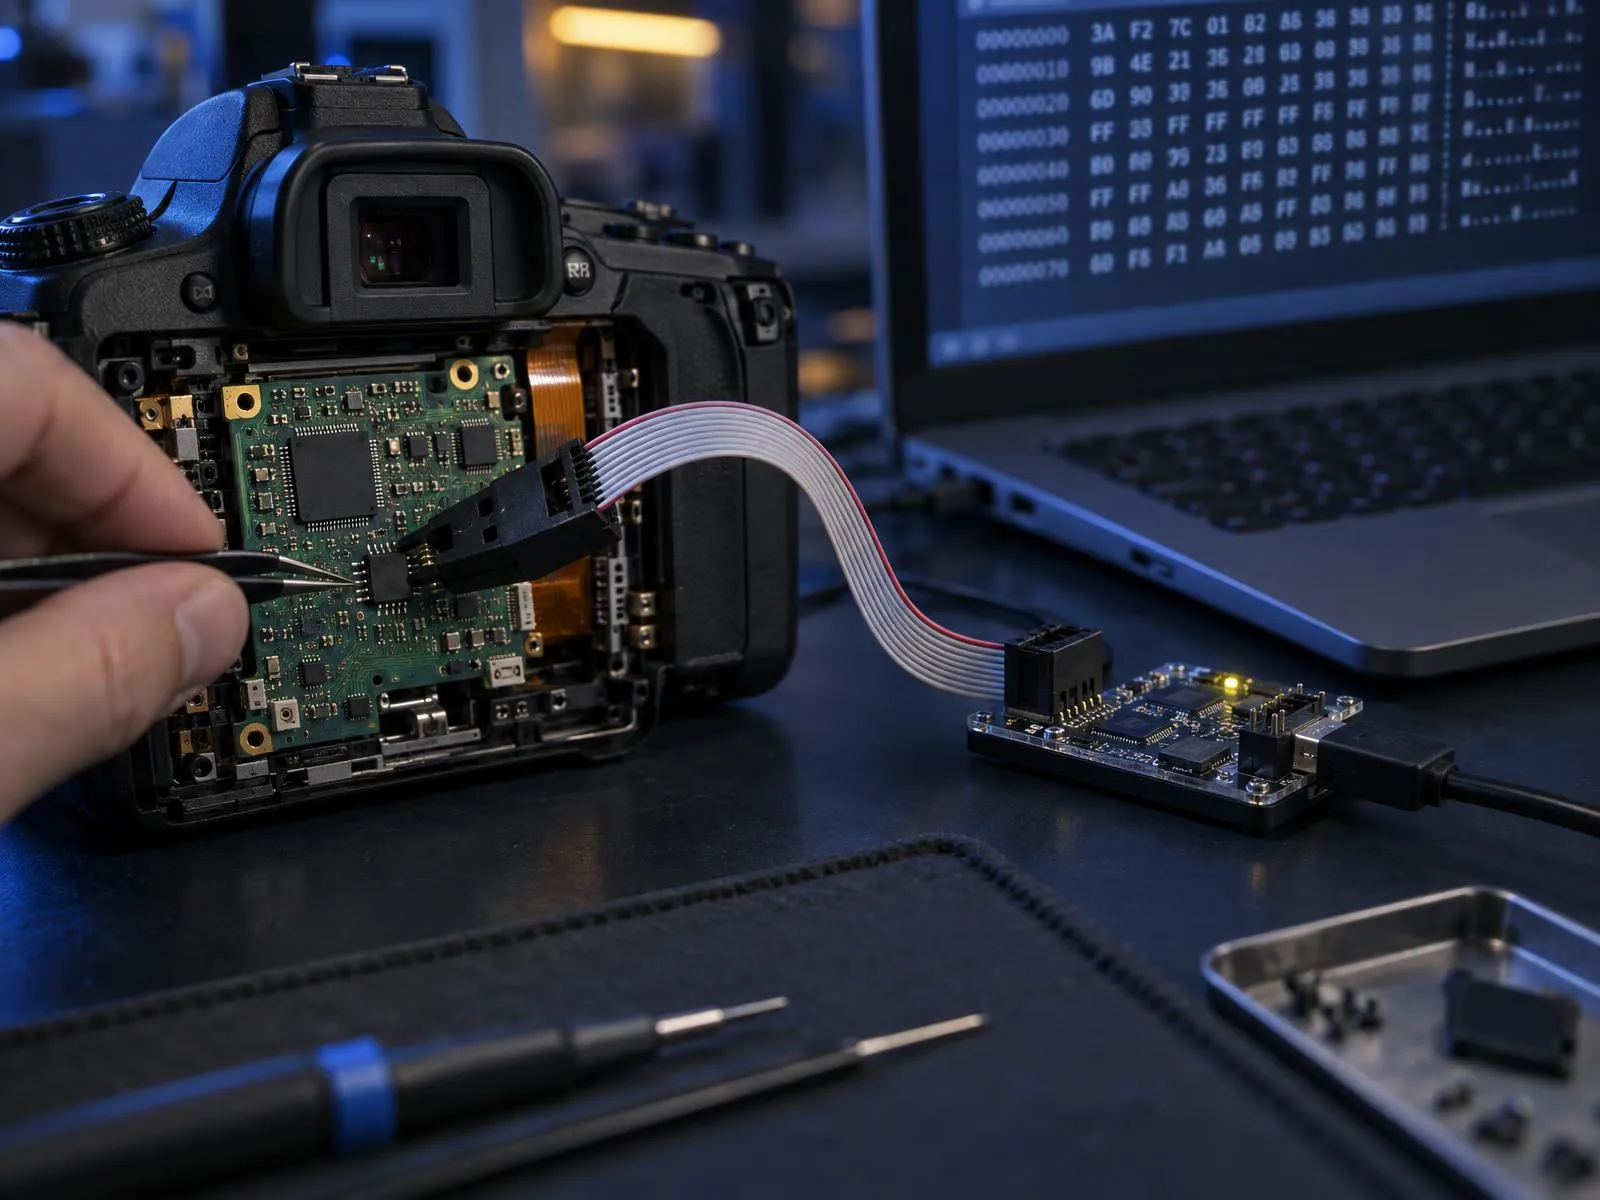
Debug ports left open, readable memory, unencrypted firmware, hard-coded keys and passwords, unverified boot: we open the product, extract and analyse the firmware, and check that a malicious update is indeed rejected.
What you receive
- Analysis of the physical interfaces
- Analysis of the firmware and components
- Verification of boot and updates
References
- OWASP ISTG v1.0.1
- OWASP FSTM