Testing laboratory and consultancy · Granges-Paccot

Book a call

Directive 2014/53/EU · Delegated Regulation (EU) 2022/30

Radio Equipment Directive (RED) and EN 18031

Since 1 August 2025, radio equipment connected to the internet must protect the network and personal data and, if it allows payments, guard against fraud. The EN 18031 standards make it possible to demonstrate this, provided you know their restrictions. Säfeli assesses your product mechanism by mechanism, helps you fix the gaps and prepares the documentation.

Cybersecurity requirements mandatory
01.08.2025
Harmonised EN 18031 standards
3
Mechanism families in EN 18031-1
11
Cyber Resilience Act takes over
11.12.2027

Who it is for

Which radio equipment is concerned

  • Connected devices

    Wi-Fi, Bluetooth, Zigbee, cellular: smart home, sensors, gateways, app-controlled devices.

  • Products for children

    Radio toys, baby monitors and childcare equipment, with parental control.

  • Wearables

    Watches, wristbands and body-worn sensors that process personal data.

  • Payments and monetary value

    Equipment that enables the transfer of money or virtual currency.

Our services

From applicability to the technical file

A structured assessment against EN 18031, with the necessary testing and documentation ready for the technical file.

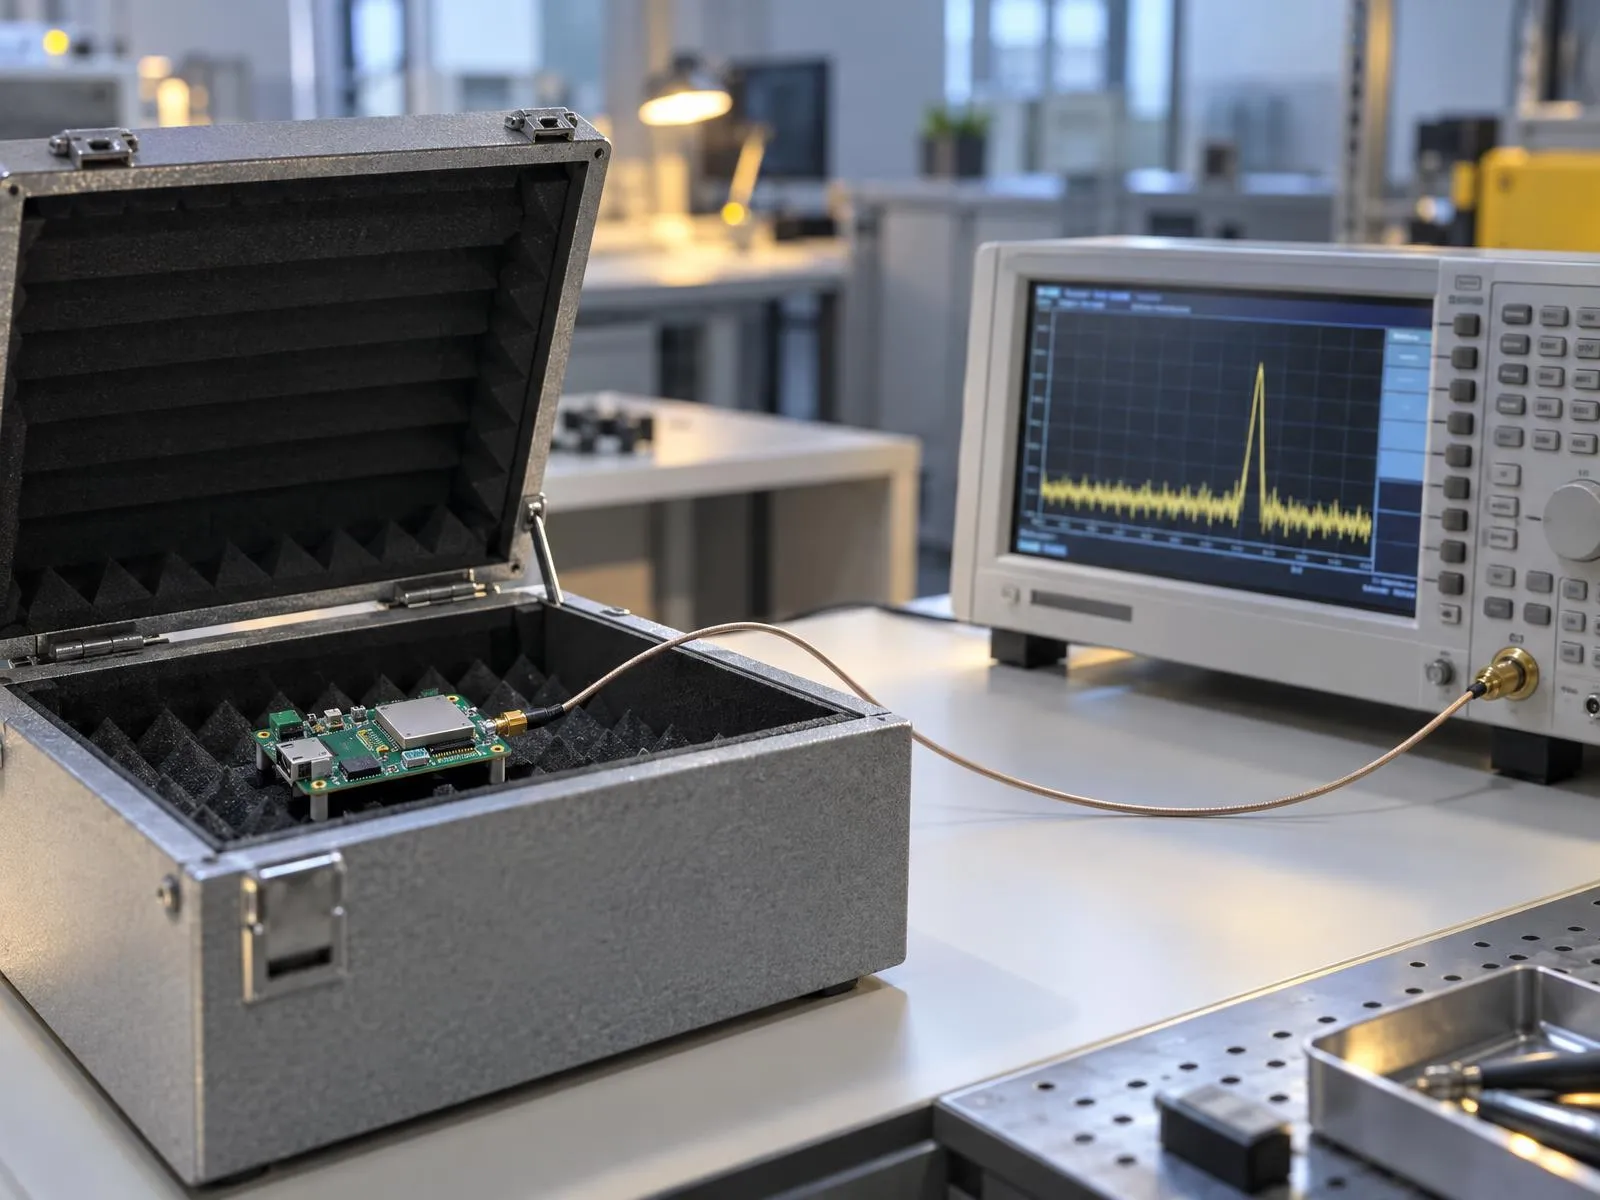
Connected device undergoing radio testing
Applicability

Which requirements apply to your product?

Internet connection, direct or via another device, data processed, payment functions: we determine which of points (d), (e) and (f) apply, which EN 18031 standards to use and which restrictions in the Official Journal affect you.

What you receive

  • Applicability analysis of points (d), (e) and (f)
  • EN 18031 standards to apply
  • Blocking points identified from the outset

References

  • Delegated Regulation (EU) 2022/30
  • Implementing Decision (EU) 2025/138
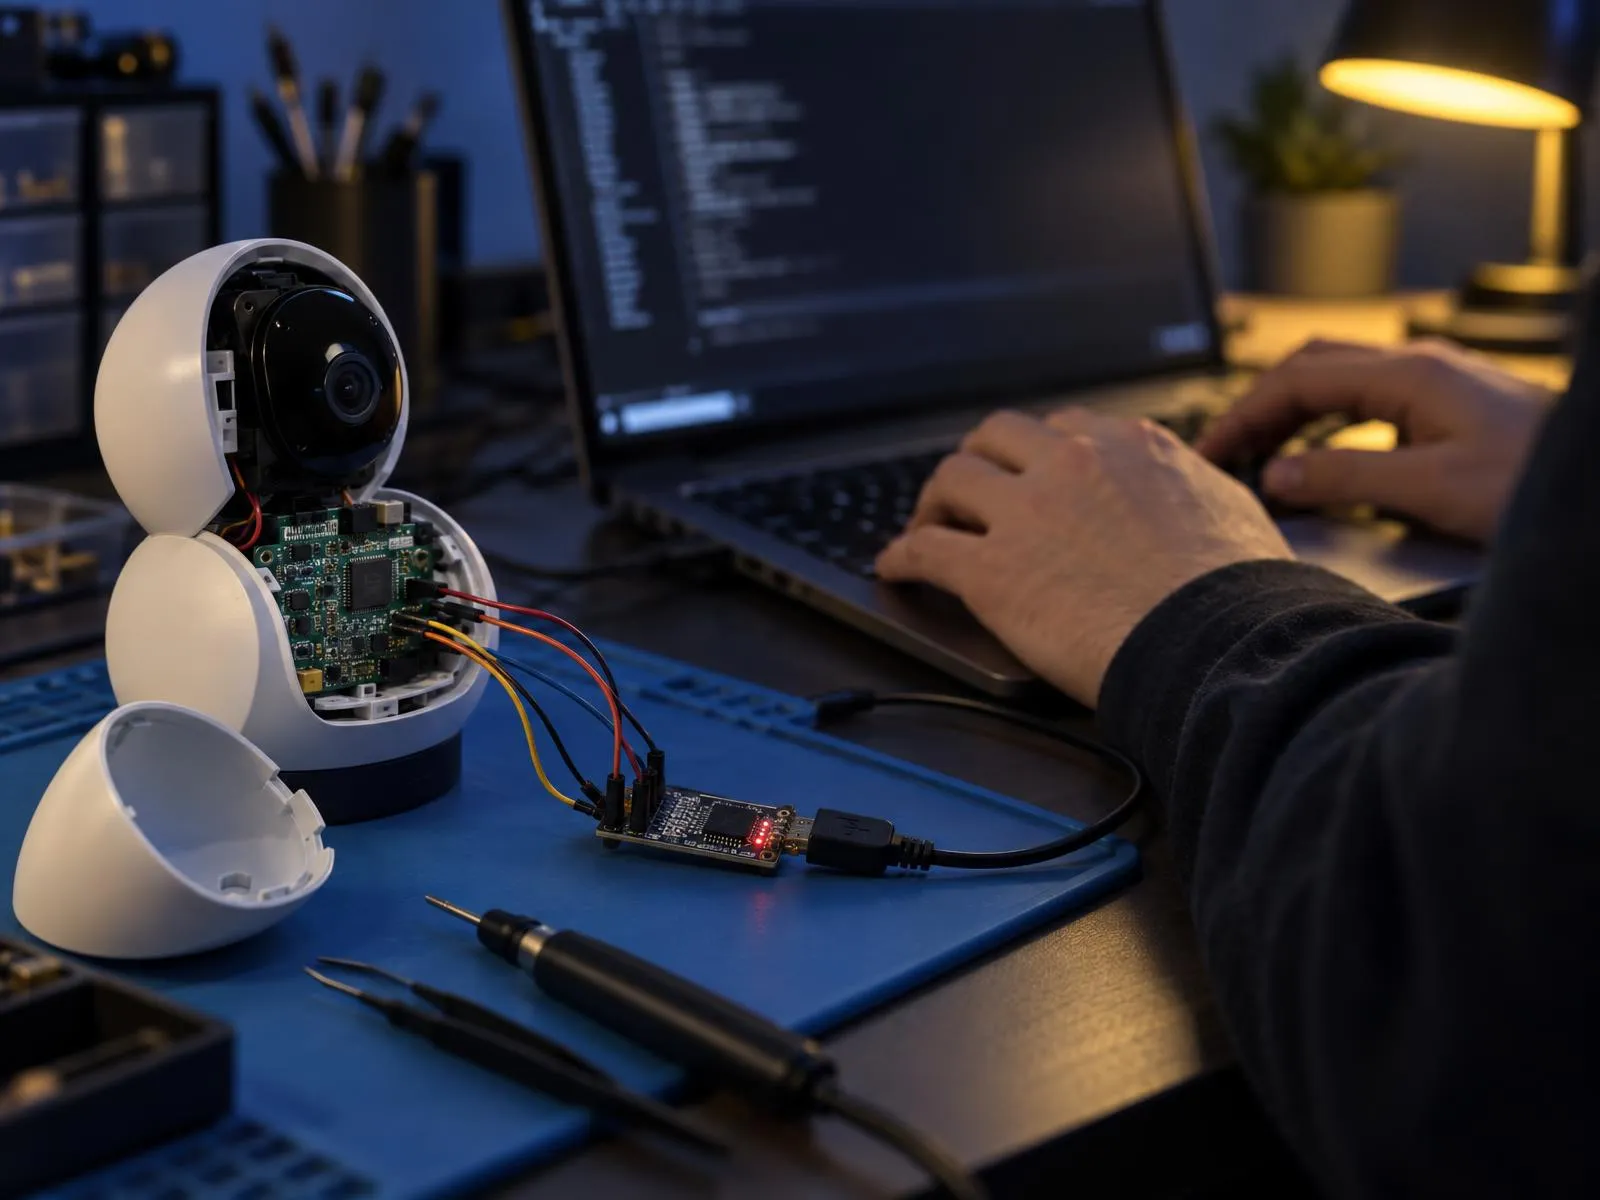
Opened connected camera linked to a computer for a security assessment
Assessment

EN 18031 assessment, mechanism by mechanism

Assets, interfaces, access control, authentication, updates, storage, communications, cryptography: we apply the decision trees of the standard to your product and document every decision on applicability and adequacy.

What you receive

  • Inventory of assets and interfaces
  • Decisions and justifications per requirement
  • List of gaps and corrective measures

References

  • EN 18031-1:2024
  • EN 18031-2:2024
  • EN 18031-3:2024
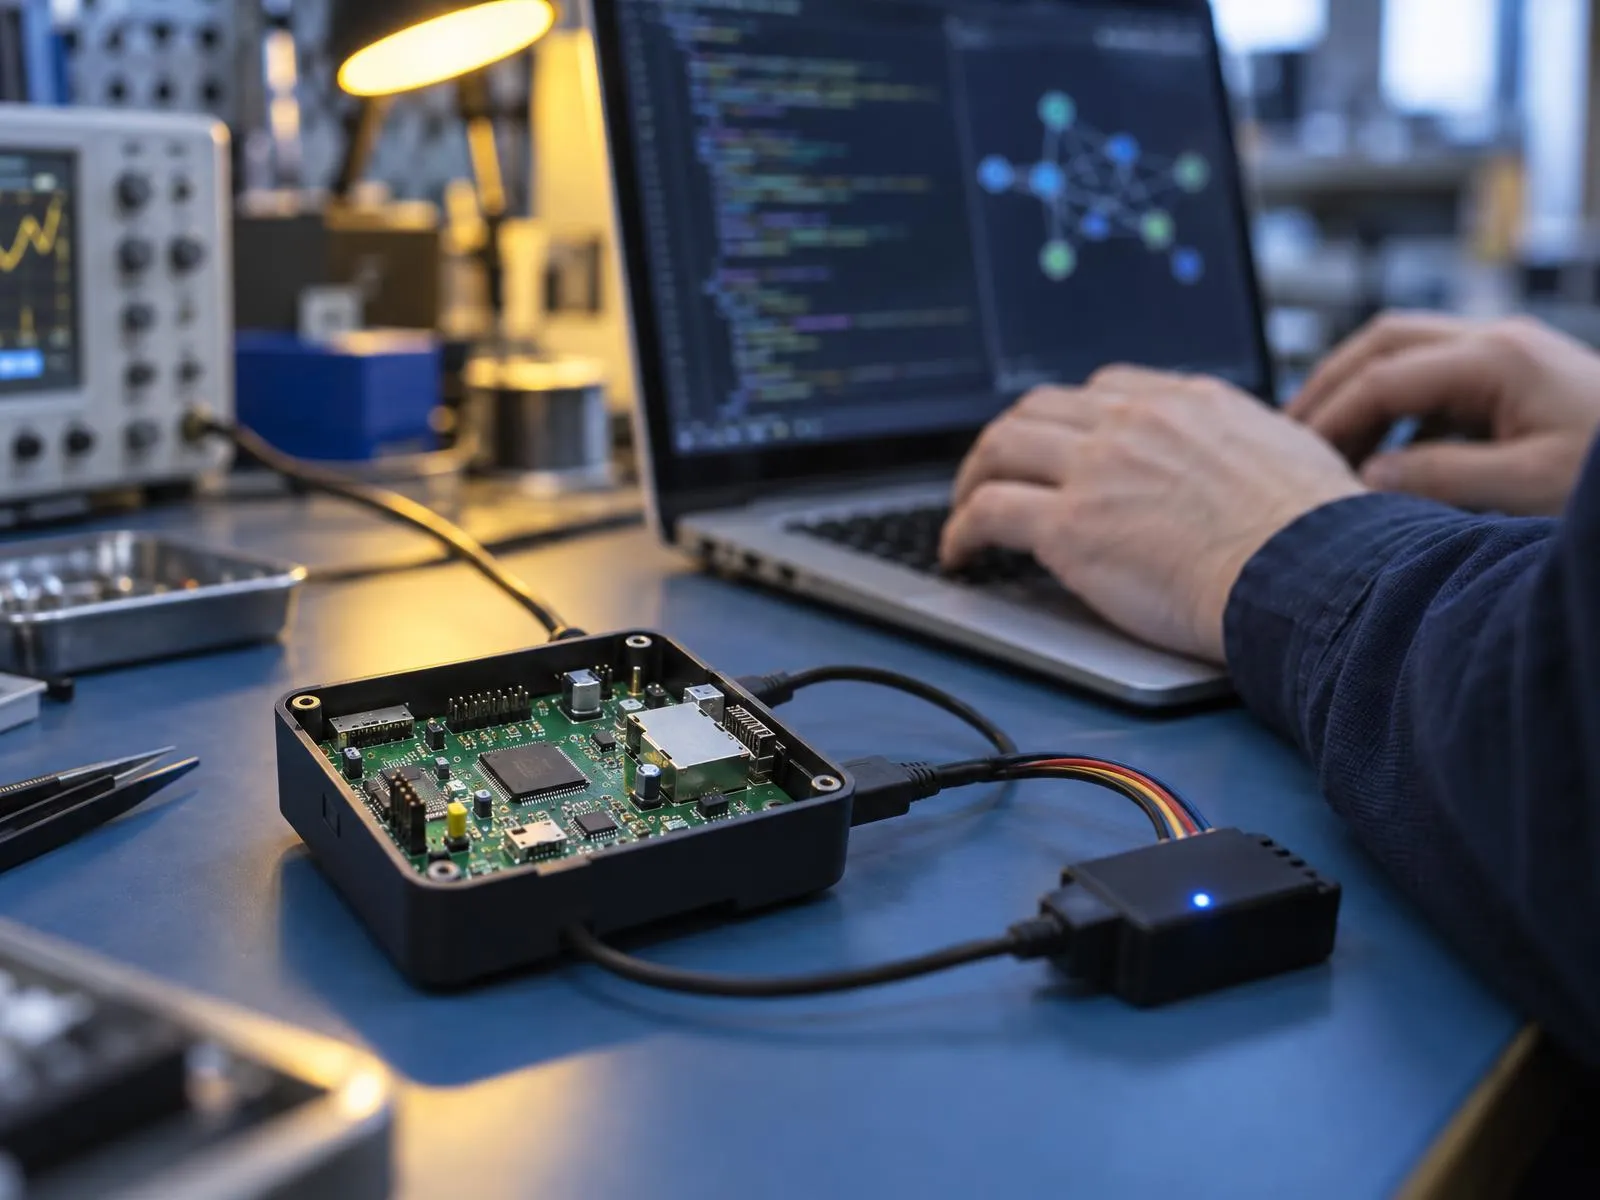
Engineer testing an electronic enclosure connected to a laptop
Testing

Product security testing

The effectiveness of the measures is verified on the product: exposed services, passwords, encryption of communications, updates, debug interfaces. Our tests confirm what the documentation states.

What you receive

  • Test plan linked to the requirements
  • Test report
  • Retest after fixes

References

  • EN 18031-1:2024, Annex A
Our product penetration testing
Consultant comparing a technical file with a list of requirements
Documentation

Documentation and EU declaration

Assessment report, justifications, test results and information for the user: we integrate cybersecurity into the RED technical file and the EU declaration of conformity, together with radio, EMC and electrical safety.

What you receive

  • EN 18031 assessment report
  • Input to the RED technical file
  • EU declaration of conformity

References

  • Directive 2014/53/EU, Art. 17 and 21
CE marking of connected products

Also

Article 3.3

The three cybersecurity requirements of the RED

Delegated Regulation (EU) 2022/30 activates points (d), (e) and (f) of Article 3.3 of the Radio Equipment Directive. Each one targets different equipment and corresponds to an EN 18031 standard.

  1. 30.01.2025EN 18031 published in the Official Journal of the EU
  2. 01.08.2025Requirements applicable
  3. 11.12.2027Cyber Resilience Act takes over
  • Art. 3.3(d) Network protection

    Any radio equipment capable of communicating over the internet must not harm the network or its functioning, nor misuse network resources.

    Delegated Regulation (EU) 2022/30, Art. 1(1); EN 18031-1
  • Art. 3.3(e) Personal data

    Connected equipment that processes personal, traffic or location data, as well as childcare radio equipment, radio toys and wearable radio equipment.

    Delegated Regulation (EU) 2022/30, Art. 1(2); EN 18031-2
  • Art. 3.3(f) Protection from fraud

    Connected equipment that enables the transfer of money, monetary value or virtual currency.

    Delegated Regulation (EU) 2022/30, Art. 1(3); EN 18031-3
  • Directly or via another device

    A Bluetooth product whose app relays the data to the cloud or delivers the updates is, in principle, communicating with the internet: it is in scope.

    Delegated Regulation (EU) 2022/30, Art. 1(1)
  • Exclusions

    Medical devices and in vitro diagnostic medical devices for all three requirements; aeronautical products, vehicles and electronic road toll systems for data protection and fraud protection.

    Delegated Regulation (EU) 2022/30, Art. 1(2) and (3), and Art. 2
  • After 11 December 2027

    The cybersecurity part of the RED is repealed and the CRA takes over. Equipment placed on the market since 1 August 2025 can still be checked against the RED.

    Delegated Regulation (EU) 2026/339

Sources: Delegated Regulation (EU) 2022/30, Art. 1 and 2; Implementing Decision (EU) 2025/138; Delegated Regulation (EU) 2026/339.

EN 18031-1

What EN 18031 checks

Eleven families of security mechanisms, assessed on the assets and interfaces of your product. EN 18031-2 adds, in particular, logging, data deletion and parental control.

  • Access control and authentication

    Who can access what, with which credentials: password strength, changing default values, protection against brute-force attacks.

    ACM, AUM
  • Secure updates

    Software update mechanism, verification of the authenticity and integrity of updates, automatic updates.

    SUM
  • Storage and communications

    Integrity and confidentiality of stored and exchanged assets, protection against replay.

    SSM, SCM
  • Resilience and network traffic

    Withstand denial-of-service attacks, monitor the network and limit malicious traffic, for network equipment in particular.

    RLM, NMM, TCM
  • Keys and cryptography

    No static confidential key by default, algorithms and protocols in line with best practice.

    CCK, CRY
  • General capabilities

    Up-to-date software with no known vulnerabilities, exposed services and interfaces kept to the strict minimum and documented, input validation.

    GEC

Standards

RED cybersecurity standards

The three EN 18031 standards have been harmonised since 30 January 2025, with restrictions. They refer to other well-known frameworks.

StatusStandardScope
HarmonisedEN 18031-1:2024Internet-connected radio equipment, Art. 3.3(d)
HarmonisedEN 18031-2:2024Equipment processing personal data, Art. 3.3(e)
HarmonisedEN 18031-3:2024Equipment processing virtual currency or monetary value, Art. 3.3(f)
MappingEN IEC 62443-4-2:2019Technical requirements for industrial components (EN 18031-1, Annex B)
MappingETSI EN 303 645 V3.1.3Cybersecurity for consumer IoT (EN 18031-1, Annex C)
ReferenceETSI TS 103 701*Test cases for ETSI EN 303 645

* Version to be checked for your project. Restrictions under Implementing Decision (EU) 2025/138: the “rationale” and “guidance” sections do not give presumption, nor do the cases described above. No new edition of EN 18031 has been published in the Official Journal of the EU to date (to be checked at the time of your project).

Restrictions

The restrictions that make a technical file fail

The EN 18031 standards are harmonised with restrictions. Knowing them from the design stage avoids having to rework the software or go through a notified body.

  • Optional passwords

    If the user can choose not to set any password, EN 18031-1 and EN 18031-2 do not give presumption of conformity.

    Implementing Decision (EU) 2025/138, clauses 6.2.5.1 and 6.2.5.2
  • Parental control

    For toys, childcare and wearable equipment, EN 18031-2 does not give presumption if parental access control is not ensured.

    Implementing Decision (EU) 2025/138, clauses 6.1.3 to 6.1.6
  • Protection from fraud

    Some assessment criteria of EN 18031-3 do not give presumption of conformity: they must be justified by other means.

    Implementing Decision (EU) 2025/138, clause 6.3.2.4
  • No presumption: a notified body

    If a standard is not applied in full, the corresponding requirement goes through EU-type examination or full quality assurance with a notified body. A well-prepared design avoids this.

    Directive 2014/53/EU, Art. 17(3) and (4)

Our approach

Your RED assessment in four steps

  1. Discovery call

    Your product, its connections, its data and your timeline. 30 minutes.

  2. Applicability

    Points (d), (e) and (f), standards to apply, restrictions and blocking points.

  3. Assessment and testing

    EN 18031 mechanisms, testing on the product, fixes with your teams.

  4. Technical file

    Assessment report, technical file and EU declaration of conformity.

Swiss market

RED cybersecurity in Switzerland

OFCOM's Ordinance on Telecommunications Installations (VFAV) adopts the cybersecurity requirements of Delegated Regulation (EU) 2022/30, applicable since 1 August 2025. The EN 18031 standards are adopted as Swiss standards: the same assessment is valid for Switzerland and for the EU.

Sources: VFAV, SR 784.101.21, Annex 1, items 7 to 9, and Art. 10b; EN 18031-1:2024, foreword.

Frequently asked questions

Frequently asked questions on RED cybersecurity

Does your product raise a specific question? Ask an engineer directly.

Book a call
Since when have the RED cybersecurity requirements applied?

Since 1 August 2025, for all radio equipment placed on the market from that date. They remain applicable until 11 December 2027, when the Cyber Resilience Act takes over.

Sources: Delegated Regulation (EU) 2022/30; Delegated Regulation (EU) 2026/339

Which EN 18031 do I need to apply?

EN 18031-1 for all radio equipment connected to the internet (network protection); EN 18031-2 if it processes personal, traffic or location data, or if it is a toy, childcare equipment or wearable equipment; EN 18031-3 if it enables payments. A single product often falls under two, or even all three, standards.

Sources: Delegated Regulation (EU) 2022/30, Art. 1; EN 18031-1, -2 and -3:2024

Is EN 18031 mandatory?

No: the requirements of the directive are mandatory, not the standard. But applying EN 18031 in full is the only route that allows the manufacturer to assess conformity with the Article 3.3 requirements itself. Without it, or with a clause subject to a restriction, a notified body is involved in the assessment.

Sources: Directive 2014/53/EU, Art. 17(3) and (4); Implementing Decision (EU) 2025/138

My product allows users not to set a password: is that a problem?

Yes, for presumption of conformity. The publication of EN 18031-1 and -2 in the Official Journal of the EU excludes this case. The simplest solution is often to rework the authentication mechanism at the design stage; otherwise, a notified body must be involved for the requirement concerned.

Sources: Implementing Decision (EU) 2025/138

How does an EN 18031 assessment work?

For each mechanism, the standard starts from the product's assets and interfaces: a decision tree establishes whether the requirement applies, then whether the implementation is adequate. The assessment is carried out at three levels: the design, the completeness of the measures, then their effectiveness, which involves examining the product from an attacker's point of view.

Sources: EN 18031-1:2024, clause 5 and Annex A

Will the work done for EN 18031 count towards the CRA?

Largely. The EN 18031 mechanisms overlap with a large part of the CRA design requirements. The CRA mainly adds the documented risk assessment, vulnerability handling throughout the support period and reporting. We build your RED file so that it serves as a basis for the CRA.

Sources: Regulation (EU) 2024/2847, Art. 13 and Annex I (comparison: Säfeli interpretation)

Do these requirements apply in Switzerland?

Yes. OFCOM's Ordinance on Telecommunications Installations adopts the cybersecurity requirements of the Radio Equipment Directive, applicable since 1 August 2025. The EN 18031 standards are also Swiss standards.

Sources: VFAV, SR 784.101.21, Annex 1, items 7 to 9, and Art. 10b

Book a call

Tell us about your radio equipment

Book a 30-minute slot with an engineer directly. No back-and-forth by email: you choose the time, we prepare the call.

Choose a time slot

Contact details

Address
Säfeli Sàrl
Route d'Englisberg 3
1763 Granges-Paccot
Languages
French, German, English
Book a call